

SmartIP Data Protection Desk · Updated September 2026
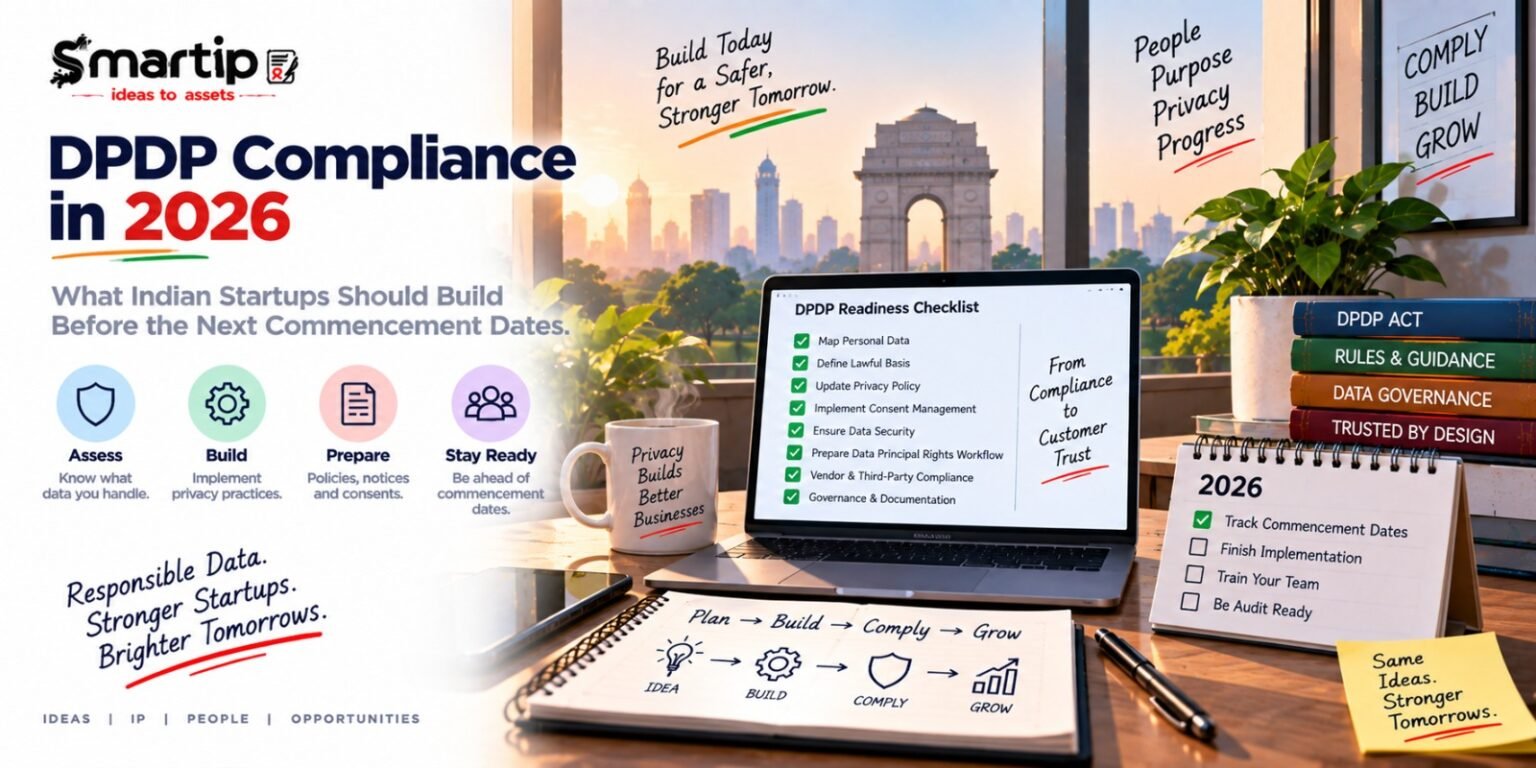
India’s DPDP regime is being brought into force in phases. This SmartIP guide explains what is already in force, what starts in November 2026 and what comes into force in May 2027, and gives startups a practical implementation roadmap.
India’s Digital Personal Data Protection Act, 2023 and the final Digital Personal Data Protection Rules, 2025 are being implemented through phased commencement rather than one single go-live date. That distinction matters to every startup planning its 2026–27 product roadmap.
As of September 2026, selected institutional and enabling provisions are already in force. A one-year phase arrives on 13 November 2026, while most substantive day-to-day obligations under the Act and Rules are scheduled for the eighteen-month point on 13 May 2027.
The implementation window should be used to change systems, not merely to draft a privacy policy. Data mapping, consent withdrawal, deletion, vendor contracting, security logging, breach response and rights handling all depend on product architecture.
Selected Act provisions and Rules 1, 2 and 17–21 commenced.
Rule 4 and the specified one-year Act provisions commence.
Most operational notice, security, rights, child, SDF and transfer provisions commence.
Use the implementation window now
Phased commencement does not mean that businesses should delay all work until 2027. Product and engineering changes can require months of planning, especially where data is spread across cloud services, analytics tools and processors.
Create a DPDP readiness programme with milestones for data mapping, product-copy review, processor contracts, rights workflows, security testing and deletion. Tie the programme to ordinary product releases so privacy improvements are implemented alongside engineering changes. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The main risk of waiting is that legal obligations arrive after the architecture is fixed. A company may then discover that consent cannot be withdrawn cleanly, that processors cannot delete data or that teams do not know where personal data is stored. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Start with a real data map
A privacy notice can describe only what the company actually understands. The data map should identify each category of personal data, its source, purpose, storage location, recipients, processors and retention logic.
Walk through the website, mobile app, CRM, support system, payments, analytics, cloud storage, recruitment, HR and any AI services. Ask engineering to verify every flow rather than relying on a policy prepared from assumptions. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
An incomplete map creates cascading problems because notice, consent, security, transfer and deletion decisions will all be based on the wrong factual picture. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Write notices as product copy
Rule 3 requires notice to be independently understandable, clear and plain, and to identify personal data and specified purposes while providing information about withdrawal, rights and complaints.
Replace generic language such as 'we use data to improve services' with purpose statements that correspond to real user interactions. Product designers should decide where notice is shown and how layered explanations work on small screens. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
A notice that lists every conceivable purpose may appear comprehensive but can undermine specificity and user understanding. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Design consent and withdrawal together
Where consent is the basis for processing, the withdrawal path should be considered when the consent flow is created. The Rules require a withdrawal route that is comparable in ease to giving consent.
Record consent state, time, notice version and downstream consequences. When consent is withdrawn, identify which processing stops, which records remain for legal reasons and which processors need instructions. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The risk is not only a poor user experience. A one-click consent followed by a difficult withdrawal process can expose a deeper architecture problem. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
A startup discovers during review that the written policy and the actual product behave differently. The team fixes the system first, then updates the notice and evidence. The lesson is that privacy compliance is strongest when legal text follows technical reality.
Build minimum security safeguards
Rule 6 specifies minimum types of reasonable security safeguards, including encryption or equivalent protective techniques where appropriate, access control, logging and monitoring, continuity measures, processor-contract safeguards and organisational controls.
Create a security-control register that shows who can access production data, how privileged access is reviewed, where logs are retained, how backups are protected and who owns incident response. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
Security claims in a policy are weak if the startup cannot show implementation evidence such as access reviews, monitoring or tested backups. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Prepare for the DPDP breach clock
Rule 7 requires affected Data Principals to be informed without delay and the Board to receive an initial intimation without delay, followed by detailed information within seventy-two hours unless a longer period is allowed.
Define incident severity, internal escalation, evidence preservation, processor notification, legal review and customer communications before an incident happens. Run a tabletop exercise using a realistic cloud or credential-compromise scenario. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
Without a rehearsed workflow, the first hours of an incident are often lost deciding who has authority to act. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Make retention executable
Privacy programmes fail when retention exists only in prose. Rule 8 contains specific erasure and retention mechanisms, including a minimum one-year retention rule for specified processing data and logs for stated purposes, subject to other law.
Create a schedule for account data, transaction records, support tickets, recruitment files, security logs, backups and processor copies. For each category, identify the deletion trigger, owner and technical job that performs erasure. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The risk is conflicting rules: one team may delete information needed for security while another retains marketing data indefinitely without purpose. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Build a rights and grievance workflow
Rule 14 requires publication of the means through which Data Principals can exercise rights and a stated grievance-redressal period that does not exceed ninety days.
Create one intake channel, an identity-verification method, internal service levels, a processor-assistance path and a record of outcomes. Test whether a user’s data can actually be located, corrected and erased where applicable. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
A rights process that depends on one engineer manually searching production databases will not scale. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Decide whether children will use the product
Rule 10 requires verifiable parental consent before processing a child’s personal data, subject to the Act and specified exemptions. This makes child use a product-design issue, not merely a legal notice issue.
Identify whether the service is reasonably likely to be used by children, what age information is necessary and whether the business can minimise processing rather than build a complex verification system. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The risk of ignoring user demographics is that the company may discover after launch that its onboarding and advertising architecture is incompatible with the child-data framework. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Understand Significant Data Fiduciary readiness
Rule 13 provides additional obligations for Significant Data Fiduciaries, including annual DPIAs and audits and due diligence concerning algorithmic software so that it is not likely to pose risks to Data Principals’ rights.
Even if a startup is not designated, high-scale or high-impact companies can borrow the same governance pattern: maintain a model inventory, run periodic risk review and keep evidence of major control decisions. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The danger is assuming that sophisticated algorithmic governance can be built instantly after a future designation. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Map transfers without oversimplifying localisation
Rule 15 permits personal-data transfers outside India subject to requirements the Central Government may specify concerning availability to foreign States or entities under their control. Rule 13 separately contemplates specified localisation-type controls for SDFs.
Maintain a transfer map showing hosting region, remote-access locations and sub-processors. Preserve architectural flexibility so the company can respond to future Government orders. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
Avoid absolute statements such as 'all DPDP data must stay in India' or 'cross-border transfers are unrestricted'; both can misstate the current framework. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
Create a 180-day readiness plan
A practical DPDP programme can be completed in stages: inventory, minimise, update notices, contract with processors, test rights, run security review and perform a mock incident.
Assign an executive sponsor, product owner and engineering owner. Track open gaps with deadlines and use quarterly privacy reviews to catch new SDKs, AI vendors and data uses. The strongest implementation connects the legal requirement to a named product owner, a real system and evidence that can be reviewed later.
The biggest implementation risk is treating privacy as a one-time legal project that becomes stale as soon as the product changes. A startup should therefore treat this as an operating-control question rather than only as wording for a policy.
A practical quarterly review
Once the initial programme is built, review it every quarter. Compare the current product architecture with the data map, processor register, retention schedule and user-facing notices. Ask whether any new AI feature, SDK, country, data field or customer use case changes the earlier analysis.
Use a short dashboard: unresolved vendor reviews, overdue deletion tests, open rights requests, untested incident actions, processing activities without owners and international flows without documented analysis. The purpose is to detect drift before it becomes a compliance or sales problem.
Privacy governance should become part of ordinary product operations. The most mature startups do not wait for an annual legal audit to discover that engineering changed six months earlier.
Questions teams commonly ask
Do small startups need a formal privacy team?
Not necessarily. Early-stage companies can assign clear responsibility across product, engineering, security and legal support. What matters is that ownership is explicit and key controls are tested.
Can a privacy policy substitute for a data map?
No. The policy should be produced from the data map. If the organisation cannot identify systems, vendors and purposes, the notice is unlikely to describe processing accurately.
How often should privacy documents be updated?
Whenever material processing changes and on a scheduled review cycle. Product launches, new AI vendors, new countries, changed retention and new user groups should trigger review.
Should every issue be treated as high risk?
No. A proportionate programme ranks activities by data sensitivity, scale, user impact, automation and regulatory exposure so stronger controls are applied where they matter most.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
A useful implementation record should also state who approved the control, when it was last tested and what evidence exists. This turns abstract compliance into a repeatable operational process and makes future audits, customer reviews and remediation much easier.
SmartIP takeaway
The practical objective is not a perfect policy library. It is a product and organisation that can explain what personal data it uses, why it uses it, who receives it, how it is protected, how people exercise rights and what happens when something goes wrong.
DPDP and GDPR differ in scope and legal structure, so they should not be collapsed into one checklist. But both reward the same operational maturity: data minimisation, accurate records, secure processors, tested rights, disciplined retention and accountable product decisions.
Official sources
- MeitY — DPDP Act Commencement Notification
- MeitY — Digital Personal Data Protection Rules, 2025
- MeitY — Digital Personal Data Protection Act, 2023
This article is for general education and awareness and does not constitute legal advice. Applicability, commencement, transfer and breach analysis depend on the facts and the law in force at the relevant time.